mehanhackeado.es: the emergency site we built for when you get hacked
By Kike Gandia · Threats · 6 min read
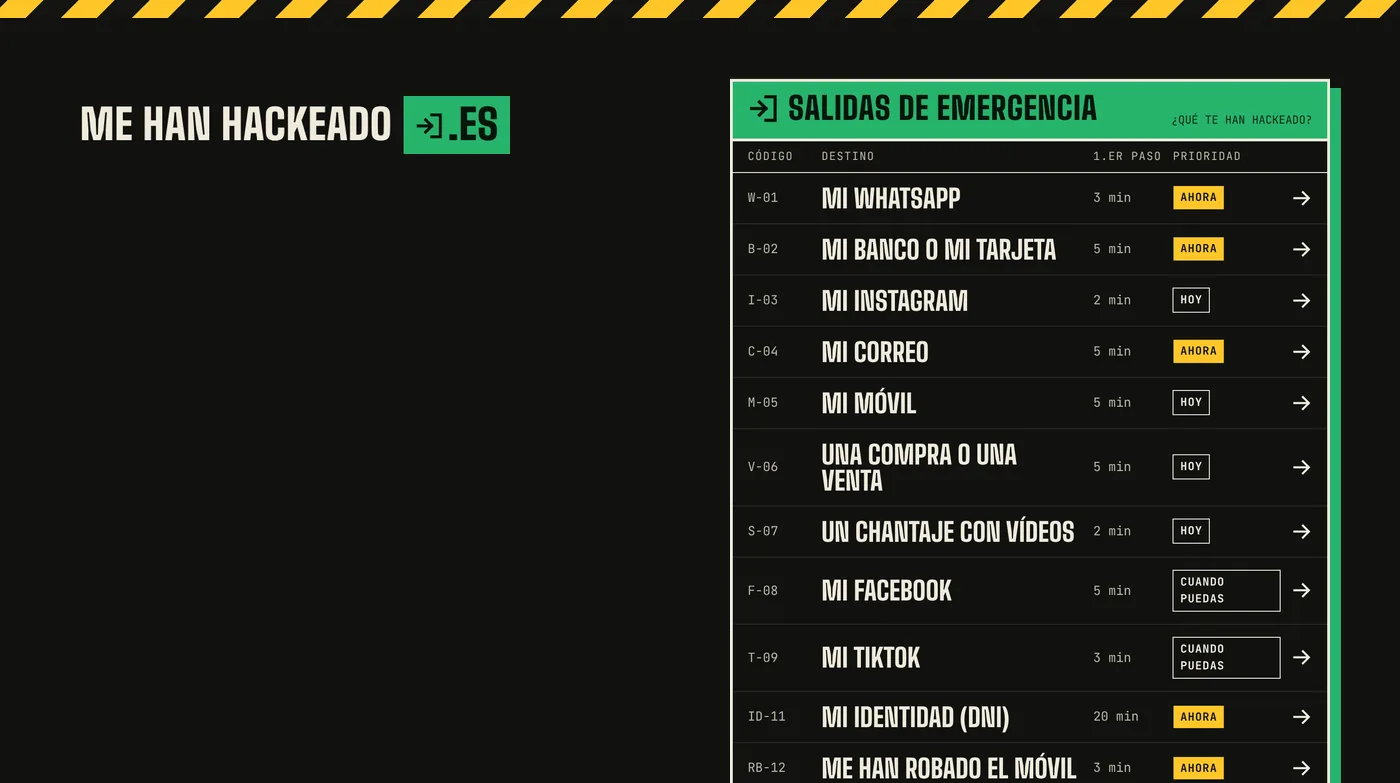
Hardly anyone gets hacked during office hours. Their WhatsApp is stolen on a Sunday night, they see a charge that is not theirs when they wake up, or at lunchtime a message arrives from «their son» on a new number. And what they find when they search for help on their phone, heart racing, is six-year-old forum threads, ten-minute videos and ads from people promising to «recover your account» for a fee: the second scam.
For that moment we built mehanhackeado.es («I've been hacked» in Spanish). It is an emergency site, written in Spanish for people in Spain, that tells you what to do in order, how long each step takes and who to call. It is free, needs no sign-up and sets no cookies without your consent. It is run by the same QuantumSec intelligence team that publishes our weekly threat landscape every Monday.
- 20
- emergency protocols (15 for individuals and 5 for companies)
- 459
- live fake websites (imitating 25 Spanish brands (report of 23 October))
- 6 h
- how often the report updates
- 0
- messages sent by the checker (it runs entirely in your browser)
mehanhackeado.es in figures, as of 24 October 2026.
What is inside
- Guides Emergency exits
- One protocol per situation: WhatsApp, bank, Instagram, email, phone, online shopping, sextortion, identity theft, leaked passwords… Each starts with the very first thing to do and continues with at most seven steps, each with its time.
- Report Scams today
- The fake websites imitating Correos, the DGT traffic authority, the tax agency, banks and energy companies right now. It updates itself several times a day and each brand has its own page: how the scam arrives, its official site and what to do if you fell for it.
- Checker Is it a scam?
- Paste the suspicious text or WhatsApp message and it tells you why it is (or is not) a scam and which guide to follow. The analysis happens on your phone: the message never leaves it.
- Channels Report it
- Who to contact and how: INCIBE's 017 helpline, online police reports with Policía Nacional and Guardia Civil, the AEPD and the Banco de España, with official links checked by hand and dated.
- First hour Companies
- Ransomware, CEO fraud, hacked websites, data leaks and the first hour of an incident: what to isolate, what to preserve and who to notify on time.
- Extras Glossary and open data
- Seventeen scam terms explained without jargon (smishing, vishing, SIM swapping, reverse Bizum…) and the report as JSON and CSV under a CC BY 4.0 licence for media and universities.
What a guide looks like
Someone who arrives frightened does not read: they scan. That is why every guide has the same shape, and the shape is part of the content.
- Top — First of all
A single sentence in yellow with the very first thing to do. «Call your bank NOW, on the number on your card». Never hidden in step four. - 30 s — The summary
All the steps in one list, with the minutes each one takes. If that is all you read, you already know where to go. - ≤ 7 — The steps
Each step starts with a verb and says how long it takes. You tick them off as you go, and your progress is stored only in your browser. - Red — Don't do this
What makes things worse: paying someone who promises to get your account back, calling the number in the text, switching the computer off before saving evidence. - After — Lock it down and report it
What to change so it does not happen again and where to report it, with the official channels block at the end of every guide.
The newest guide covers the «Hola mamá» scam (a fake child asking for money) and brings something new: the scammer's chat plays out in front of you, message by message, and each red flag is marked the moment it appears. At the end it asks what you would do. It is the fastest way we know to help someone recognise the trick the next time it reaches them for real.
The situations you are most likely to need
| What happened | The guide | First thing to do |
|---|---|---|
| Your WhatsApp was stolen | My WhatsApp | Re-register your number with the SMS code: the intruder is locked out. |
| Charges that are not yours, or you entered details on a fake site | My bank or my card | Call your bank on the number on your card, never the one in the text. |
| «Your son» asks for money from a new number | The «Hola mamá» scam | Do not pay: call him on his usual number. |
| Your phone was stolen | My phone was stolen | Lock it remotely and call your carrier to block the SIM. |
| Someone is blackmailing you with intimate videos | Video blackmail | Check whether it is the usual mass email: it almost always is. |
| The company's computers have been encrypted | Ransomware | Isolate without switching off, and call professionals and INCIBE-CERT. |
| Your company's email was spoofed to collect an invoice | CEO fraud | Ask the bank to try to recover the transfer. |
The scam report: where it comes from
Every six hours our intelligence system cross-checks public lists of malicious domains against the 33 most impersonated Spanish brands. It only publishes a site if it is fake by construction: it carries the brand's name and does not belong to it. A legitimate site that has been compromised is never listed, because naming it would harm one more victim. Addresses are shown defanged, with [.] instead of the dot, so nobody can open them by mistake.
On 23 October there were 459 live fake websites imitating 25 brands. The figure changes every day, which is why the home page shows a live counter and estafas-hoy breaks it down brand by brand.
If it is happening to you now. Open mehanhackeado.es and choose what has been hacked. If you would rather talk to a person, INCIBE's 017 helpline is free and confidential, from 8:00 to 23:00 every day. If it is your company, also follow our guide to the first 24 hours.
A help site cannot be another risk
A site that receives people who have just been scammed is an attractive target, so we built it the way we would build a client's site that we were going to audit afterwards:
- It is static: there is no server or database to attack, and no forms that store what you type.
- A strict hash-based CSP and Trusted Types on every page: only code we have signed runs. If a dependency tried to load an outside script, the build stops on its own.
- Analytics only with consent: nothing is downloaded from Google until you click «Accept», and «Reject» sits at the same level.
- The checker sends nothing, with or without cookies: whatever you paste stays on your phone.
For companies: keep it within your staff's reach
Almost every guide starts the same way: someone who believes it. A parcel text, a call «from the bank», an urgent email from the boss. That is why mehanhackeado.es is also useful inside a company:
- Share it with your staff: it is the link someone needs at 11 p.m., when there is nobody from IT to call.
- Use the report as a weekly reminder: which brands are being impersonated this week is the best awareness reminder there is, because it is real.
- Put it on your website: there is a badge with the live report for town councils, associations, professional bodies and media.
And if you want to go beyond a link, that is what we do at QuantumSec: security awareness training for employees built on cases like these, phishing simulations and social engineering exercises that measure who falls for it before anyone does for real, and training for technical teams and management. The mehanhackeado.es guides teach what to do once it has happened; training exists so that it does not.
Why we do it
We spend our days attacking companies, with permission, so that criminals do not get there first. We see up close how little it takes to deceive a person and how much it costs afterwards. mehanhackeado.es is the part of that work we can give away: what we would tell a friend who called us in a panic, written once, properly, for everyone.
Spotted something out of date or missing a guide? Write to us. And if it helped you, share it: the best defence against a scam is having someone tell you about it first.
Related service
employee security awareness training
Topics
#mehanhackeado-es #Scams #Phishing #Smishing #Incident-response #Awareness
Keep reading
- Bybit Hack Analysis (III): Implications and the Future of Crypto Security After the Bybit Hack
- Elite hunters: threat hunting as a strategic advantage