Honeypots and canary tokens: defending corporate networks against sophisticated adversaries
By Kike Gandia · Threats · 9 min read
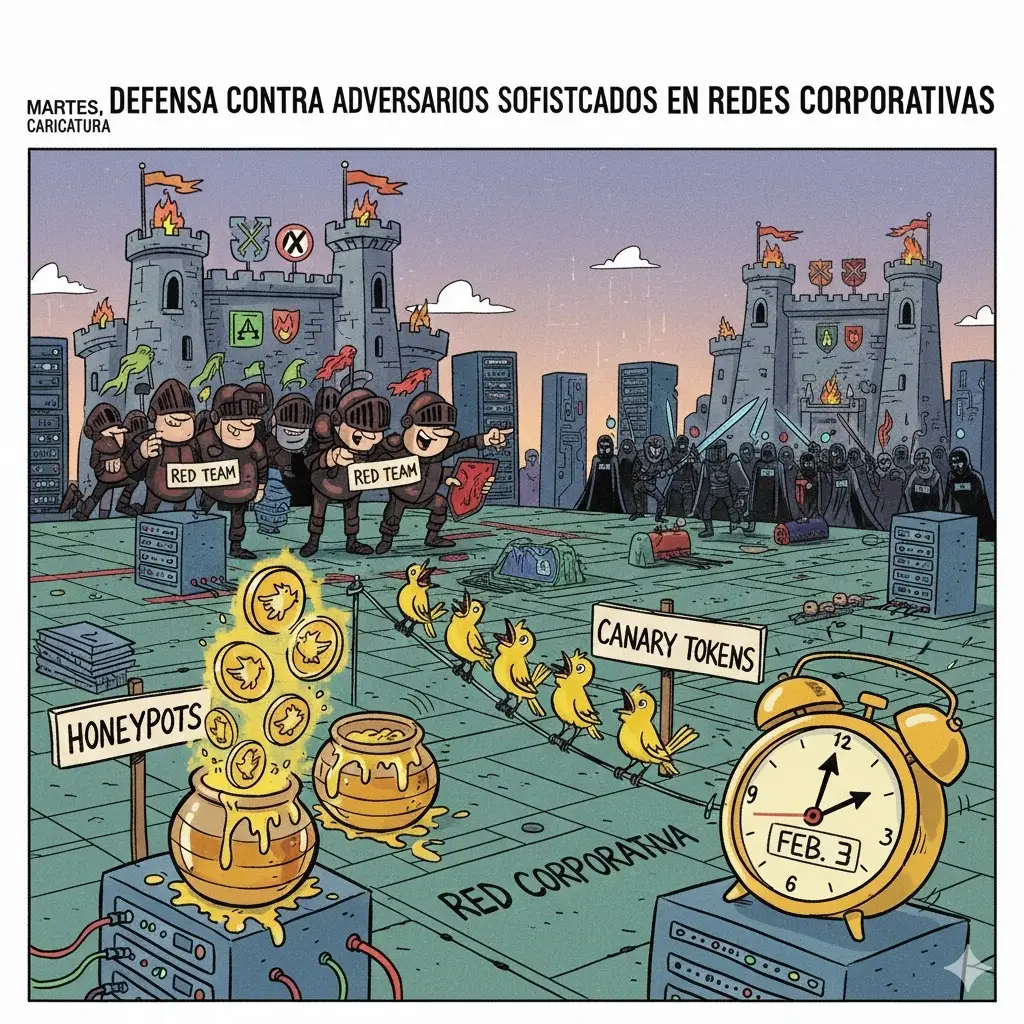
Deployed strategically, deception technology delivers one of the highest signal-to-noise ratios in defensive cybersecurity, with near-zero false positives and the ability to detect sophisticated attackers in the early stages of the kill chain. This report is a complete technical guide to deploying honeypots and canary tokens in Windows AD + Linux environments, with a focus on open-source, low-cost tools that are highly effective against professional red teams and APTs.
- ~0
- false positives: any interaction with a decoy is malicious activity
- 90%
- of traffic aimed at honeypots hits port 445 (SMB)
- 23+
- canary token types available in the free service
- 3.5M
- login attempts in 3 months against an exposed RDP honeypot (Blumira research)
The figures the article breaks down below, at a glance.
OpenCanary: the foundation for internal detection
OpenCanary, developed by Thinkst (the makers of the commercial Canary), is the ideal starting point for any corporate deception program. Its minimalist architecture lets you run it on a Raspberry Pi or a minimal VM with less than 512MB of RAM.
Recommended services for a corporate network
| Service | Port | Detection use case |
|---|---|---|
| SMB | 445 | Lateral movement (90%+ of malicious traffic) |
| RDP | 3389 | Compromised remote access |
| SSH | 22 | Brute force, Linux pivoting |
| MySQL/MSSQL | 3306/1433 | Data exfiltration |
| HTTP | 80 | Internal web reconnaissance |
| Portscan | - | Scan detection (requires iptables) |
The optimal configuration puts SMB ahead of every other service, since research shows that 90% of traffic aimed at honeypots hits port 445. Medium Here is an example of an effective JSON configuration:
{
  "device.node_id": "backup-srv01",
  "smb.enabled": true,
  "smb.auditfile": "/var/log/opencanary_smb.log",
  "ssh.enabled": true,
  "mysql.enabled": true,
  "http.enabled": true,
  "http.skin": "nasLogin",
  "portscan.enabled": true
}
The nasLogin skin emulates a Synology NAS, a frequent target for attackers looking for centralized storage. Critical practice: use realistic hostnames such as backup-srv01 or fin-db-03 that match the environment's naming conventions.
Canarytokens: digital tripwires with zero false positives
Canary tokens work as silent alarms that fire only when an adversary interacts with them. The free canarytokens.org service offers more than 23 token types, but for sensitive corporate environments, self-hosting with Docker is preferable:
git clone https://github.com/thinkst/canarytokens-docker
cd canarytokens-docker
# Set CANARY_DOMAINS and CANARY_PUBLIC_IP
docker compose up -d
The most effective tokens against sophisticated adversaries:
Microsoft Word/Excel documents with embedded URLs are highly effective because attackers routinely open documents they find during reconnaissance. Names like passwords.xlsx, AWS-credentials.docx or VPN-Password-Reset.docx all but guarantee interaction.
DNS tokens work even when the attacker has no direct HTTP access, since all they need is DNS resolution. They are ideal for embedding in bash_history files, SSH configurations or PowerShell scripts.
AWS key tokens generate fake API credentials that raise an alert whenever they are used, anywhere in the world. GitGuardian's ggcanary tool scales up to 5,000 tokens for large organizations. The AWS Infrastructure Canarytoken Terraform module deploys S3 buckets, DynamoDB tables and Secrets Manager secrets as decoys.
Strategic placement of honey files
- Root of SMB shares (ransomware's first target)
- SYSVOL/NETLOGON folders
- Backup directories with names like C:\Backup\ADBackup
- Desktops of honey admin accounts
- Migration folders (attackers hunt for legacy artifacts)
- Active Directory–specific deception
Detecting attacks against AD is one of the most valuable uses of deception technology, because techniques such as Kerberoasting, DCSync and credential dumping produce zero false positives when honeypot accounts are involved.
Honey SPNs to detect Kerberoasting
The most effective technique is to create decoy service accounts with Service Principal Names that any attacker running tools like Rubeus or GetUserSPNs.py will try to crack:
# Create the honeypot service account
New-ADUser -Name "svc_sqlbackup" -SamAccountName "svc_sqlbackup" `
  -AccountPassword (ConvertTo-SecureString -AsPlainText "RandomPasswordOf128Characters..." -Force) `
  -Enabled $true -PasswordNeverExpires $true

# Make it look privileged (attracts attackers)
Set-ADUser -Identity svc_sqlbackup -Replace @{adminCount=1}

# Register an attractive SPN
Set-ADUser -Identity svc_sqlbackup -ServicePrincipalNames @{Add="MSSQLSvc/sql-backup.domain.local:1433"}
The password must be 128+ random characters so that it is impossible to crack. Monitor Event ID 4769 (Kerberos Service Ticket Operations), filtering on the honeypot SPN. Any TGS request for this account is confirmed malicious activity.
Honey hashes in LSASS
The runas /netonly technique lets you inject fake credentials into LSASS memory, which Mimikatz will then extract along with the real ones:
runas /user:administrator@contoso.com /netonly cmd.exe
# Enter a fake password when prompted
This creates an authentication token stored in LSASS. For persistence, use the New-HoneyHash.ps1 script from the Empire project: Microsoft Community Hub
New-HoneyHash.ps1 -Domain contoso.com -Username HoneyAdmin -Password FakeP@ss123
Powershell -windowstyle hidden -noexit -file C:\New-HoneyHash.ps1
Any authentication attempt with these credentials confirms that memory has been dumped. Monitor Event ID 4625 (failed logon) and 4624 (successful logon) for the honey account.
Detecting DCSync with Deploy-Deception
Samrat Ashok's Deploy-Deception PowerShell module lets you create decoy AD objects with auditing configured automatically:
Import-Module Deploy-Deception.psd1

# Create a fake Domain Admin with DenyLogon protection
Create-DecoyUser -UserFirstName dec -UserLastName da -Password Pass@123 |
  Deploy-PrivilegedUserDeception -Technique DomainAdminsMemebership -Protection DenyLogon -Verbose

# Create an account with replication rights (detects DCSync)
Create-DecoyUser -UserFirstName dec -UserLastName da -Password Pass@123 |
  Deploy-PrivilegedUserDeception -Technique DCSyncRights -Protection LogonWorkStation nonexistent -Verbose
Detecting DCSync requires monitoring Event ID 4662 (Directory Service Access) for the replication GUIDs:
- DS-Replication-Get-Changes: 1131f6aa-9c07-11d1-f79f-00c04fc2dcd2
- DS-Replication-Get-Changes-All: 1131f6ad-9c07-11d1-f79f-00c04fc2dcd2
Realistic honeypot accounts that fool red teams
Sophisticated attackers check whether an account is legitimate before using it. Research by Sean Metcalf (Trimarc Security) identified the key attributes red teams examine:
Attributes that give fake accounts away
- Creation date identical to PwdLastSet (new accounts)
- logoncount = 0 (never used)
- Null LastLogonTimeStamp
- No associated user account for admins
How to maximize realism
- Reuse old accounts: accounts that are 10–15 years old are more believable than freshly created ones
- Generate a logon history: create a scheduled task that logs on periodically
- Simulate bad password attempts: add realistic failed attempts
- Restrict with LogonWorkstations: limit logons to nonexistent hosts as a safeguard
- Use the smart card trick: enabling and then disabling "smart card required" randomizes the password to 120+ characters
Javelin Networks' HoneypotBuster, a tool built for red teams, shows exactly which checks attackers run: validating SPNs against real computer accounts, checking timestamp consistency across DCs, and verifying logoncount.
T-Pot: an all-in-one platform for maximum coverage
T-Pot from Deutsche Telekom Security bundles more than 20 containerized honeypots with an integrated ELK Stack, real-time attack maps and Suricata as an IDS. Version 24.04.1 (January 2025) includes LLM-based honeypots (Beelzebub, Galah) that generate dynamic, context-aware responses.
Resource requirements
| Component | Minimum | Recommended |
|---|---|---|
| RAM | 8GB | 16GB+ |
| Disk | 128GB SSD | 256GB SSD |
| CPU | 4 vCPU | 8 vCPU |
Deployment modes
- Hive: full installation with ELK, dashboards and every honeypot
- Sensor: honeypots only, shipping logs to a central Hive (8GB RAM is enough)
- Distributed: multiple sensors reporting to a centralized Hive
For internal corporate networks, T-Pot may be overkill for basic detection. It is, however, ideal for:
- DMZ segments
- Research labs
- Centralized threat intelligence
- Environments that require malware analysis (Dionaea captures samples)
Keeping red teams from spotting your honeypots
Research by Vetterl & Clayton (WOOT '18) identified 7,605 honeypots through systematic fingerprinting. Sophisticated attackers know these techniques:
OpenCanary/Cowrie indicators to remove what gives the decoy away
- Cowrie: delete or rename the /home/richard directory (botnets check for it specifically).
- Default configurations left unchanged.
- Network latency in multiples of 10ms (a giveaway for virtual honeypots such as HoneyD). ResearchGate
- VMware/VirtualBox MAC prefixes (00:0C:29, 08:00:27).
Effective countermeasures what to do before going to production
- Customize immediately: change default usernames, hostnames and banners.
- Use high-interaction honeypots where possible: a real OS with real applications is harder to fingerprint.
- Add realistic activity: scheduled tasks that simulate users, background DNS/NTP traffic.
- Test with attacker tooling: run Nmap OS fingerprinting and p0f before going to production.
- Rotate services periodically: changing which services are active makes correlation harder.
Vetterl and Clayton identified 7,605 honeypots through fingerprinting: these are the telltale signs and how to counter them.
For dynamic responses that confuse automated tools, T-Pot's LLM honeypots (Beelzebub, Galah) generate context-aware output that varies with every interaction.
SIEM integration for actionable alerts
Honeypots are only as effective as the alerts that reach your response teams. The three main platforms have documented integration patterns:
ELK Stack
T-Pot ships with a preconfigured Elastic Stack. For custom integrations:
Honeypot → Filebeat (JSON logs) → Logstash → Elasticsearch → KibanaSplunk
Use the HTTP Event Collector (HEC) to ingest Canarytokens webhooks:
curl -k https://splunk:8088/services/collector \
  -H "Authorization: Splunk <token>" \
  -d '{"event": "canary alert data"}'
The official Thinkst Canary Add-on (app/6195) and Thinkst Canary App (app/6196) on Splunkbase provide predefined dashboards.
Wazuh
Wazuh integrates through an agent on the honeypot host that ships logs to the Wazuh Server. The Wazuh-Cowrie-Honeypot-Lab GitHub project includes custom decoders and rules for honeypot events.
Get alert priority right. Since any interaction with a honeypot indicates malicious activity, every alert should be Critical/High. There is no need for tuning to reduce noise — the noise is the signal.
Recommended deployment architecture
Strategic placement maximizes coverage with minimal resources:
Priority segments
- Close to the crown jewels: the same VLAN as domain controllers, database servers and sensitive file servers
- Server segments: one honeypot per main server VLAN
- Internal DMZ: detect pivoting from semi-trusted systems
- User network: detect insider threats and early lateral movement
Firewall rules for honeypot segments
Ingress (allow)
- Forward ports 1–64000 for maximum capture, or selectively per service
Egress (critical for containment)
- Allow DNS (53) for malware analysis
- Block everything else – prevent a compromised honeypot from being used as an attack platform
- Consider a proxy so outbound traffic can be analyzed
Management ports (restrict to trusted IPs)
- SSH: 64295 (T-Pot default)
- Web UI: 64297 (T-Pot default)
Recommended number of honeypots
| Organization size | Count | Placement |
|---|---|---|
| Small (<100 users) | 1-3 | DMZ, server VLAN, user VLAN |
| Midsize (100-1000) | 5-10 | One per main segment |
| Enterprise (1000+) | 10-50+ | Per VLAN/subnet + DMZ |
Automating deployment
Ansible
The ansible-cowrie-rootless project deploys Cowrie on AWS, Azure and DigitalOcean. T-Pot includes Ansible playbooks in cloud/ansible/ for distributed deployments:
cd ~/tpotce
ssh-keygen
ssh-copy-id -p 64295 user@sensor_ip
./deploy.sh  # Runs the playbook automatically
Terraform
T-Pot provides Terraform configurations in cloud/terraform/ for AWS and Open Telekom Cloud, which can be extended to other providers.
Docker Compose
T-Pot uses Docker Compose with several editions:
- standard.yml - Full suite
- sensor.yml - Distributed sensors only (4GB RAM)
- mini.yml - Lightweight deployment
- customizer.py - Builds custom configurations
Specific detection use cases
Detecting internal reconnaissance
Port scanning: OpenCanary with portscan.enabled alerts on any connection to monitored ports. Artillery automatically blacklists IPs that connect to trap ports.
AD enumeration (BloodHound/SharpHound): honeypot users with attractive names (BackupAdmin, svc_Finance) that generate Event ID 4662 when their properties are read. Any LDAP query against these objects indicates enumeration.
Detecting lateral movement
SMB lateral movement: Dionaea and OpenCanary SMB detect any attempt to connect to shares. Create attractive shares such as \\honeypot\Finance_Backup.
Pass-the-Hash/Ticket: honey hashes injected into LSASS raise an alert when they are used to authenticate. Monitor Event ID 4624 Type 3 (network logon) for the honey account.
RDP lateral movement: Blumira research documented 3.5 million login attempts in 3 months against an exposed RDP honeypot. OpenCanary RDP or Heralding capture the credentials attempted.
Detecting credential harvesting
Kerberoasting: honey SPNs with Event ID 4769 (TGS request) monitoring, where encryption type = 0x17 (RC4-HMAC) indicates an active attack.
LSASS dumping: honey hashes present in memory will be extracted along with the real credentials. Any subsequent use = confirmed dump.
NTDS.dit access: file integrity monitoring + canarytokens in documentation that references backup locations.
Detecting exfiltration
Beaconing honey files: Word/Excel documents with canarytokens that send a notification when they are opened outside the corporate environment.
DNS exfiltration: DNS tokens detect attackers using DNS tunneling to exfiltrate data, since any resolution of the honeypot FQDN triggers an alert.
Open-source tools compared
| Tool | Maintenance | Ease of use | Detection | Resources | Effectiveness vs. APTs |
|---|---|---|---|---|---|
| T-Pot | ★★★★★ | ★★★☆☆ | ★★★★★ | High (16GB) | ★★★★★ |
| OpenCanary | ★★★★☆ | ★★★★★ | ★★★★☆ | Very low | ★★★☆☆ |
| Canarytokens | ★★★★★ | ★★★★★ | ★★★★☆ | Minimal | ★★★★★ |
| Cowrie | ★★★★☆ | ★★★☆☆ | ★★★★☆ | Low | ★★★★☆ |
| Dionaea | ★★★☆☆ | ★★★☆☆ | ★★★★☆ | Low-Med | ★★★☆☆ |
| Deploy-Deception | ★★★☆☆ | ★★★★☆ | ★★★★★ | Minimal | ★★★★★ |
| qeeqbox/honeypots | ★★★★☆ | ★★★★★ | ★★★★★ | Low | ★★★☆☆ |
HoneyD is obsolete (last release in 2007). qeeqbox's honeypots Python package offers 30 protocols in a single PyPI package as a modern alternative.
Implementation plan by priority
- Weeks 1-2 — Immediate implementation
Self-hosted Canarytokens, honey files on the main shares and the first honeypot accounts in Active Directory: things you can deploy in days that start detecting right away. - Weeks 3-4 — Expanding coverage
OpenCanary on each VLAN with SMB, RDP and SSH, plus honey hashes in LSASS on domain controllers and privileged workstations. - Month 2 — Advanced detection
T-Pot in the DMZ or a lab, Deploy-Deception for full AD objects, and DCSync detection with trap objects.
The recommended order for rolling out deception; each phase is detailed below.
Phase 1: Immediate implementation (Weeks 1-2)
- Deploy self-hosted Canarytokens
- Create 3–5 honey files on the main network shares
- Set up 3 AD honeypot accounts (BackupAdmin, svc_Finance, IT_Support)
- Create 1 honey SPN to detect Kerberoasting
- Integrate alerts with your existing SIEM
Phase 2: Expanding coverage (Weeks 3-4)
- Deploy OpenCanary as 1 honeypot per main VLAN
- Configure SMB, RDP and SSH on each instance
- Implement honey hashes in LSASS on DCs and privileged workstations
- Create honey shares with attractive names
Phase 3: Advanced detection (Month 2)
- Evaluate T-Pot for the DMZ or a research lab
- Implement Deploy-Deception for full AD objects
- Set up DCSync detection with trap objects
- Add Cowrie for in-depth analysis of SSH sessions
- Document and automate deployment with Ansible/Terraform
Conclusion
Deception technology gives defenders an asymmetric advantage against sophisticated adversaries: attackers have to evaluate every asset they find, while defenders only need to wait for someone to touch a decoy. Combining OpenCanary for network detection, Canarytokens for files and credentials, and AD honeypot objects covers the full spectrum of attack techniques with minimal investment.
The key to success lies in realism and strategic placement. Accounts with a consistent logon history, files with realistic organizational names and honeypots whose hostnames match the environment's conventions maximize the likelihood of interaction while minimizing the risk of detection by sophisticated attackers, who routinely check legitimacy before exploiting any resource.
Related service
Penetration testing and ethical hacking services
Topics
#AI #Cybersecurity #Maritime-OT-ICS-Cybersecurity #HONEYPOT #Industrial-IoT #Industrial-Hardware-Security
Keep reading
- MCP: Blind Trust, Maximum Risk
- V-JEPA 2: the new visual brain that learns the world in order to anticipate it
- Hardware Analysis Series – Part 6 Bus Pirate: From Bits to Buses
- How to Share Credentials and Encrypted Files Securely with Third Parties
- How a principled hacker exploited a hole in Solana to fund indie projects